Governance
Strong governance is the foundation for how DNOW manages risk, conducts business and creates long-term value. Our governance framework defines clear accountability, from Board committees through operational management, and keeps oversight effective as the organization grows.
Corporate Governance Snapshot
The information below highlights key governance, ethics, compliance, cybersecurity and risk management disclosures from DNOW's 2025 Sustainability Report: Stronger Together. For complete details and reporting methodologies, please review the full report.
Governance Highlights
1 Diverse indicates directors that are a member of an underrepresented racial/ethnic group.
Note: Board diversity is as of December 31, 2025.
| Average Director Age | |
|
| Average Director Tenure | |
|
| Material Cybersecurity Incidents in 2025 | |
|
Board of Directors
The Board of Directors oversees DNOW’s corporate strategy, risk management and capital allocation on behalf of shareholders. Directors bring experience spanning the energy sector, logistics and supply chain, finance, technology, cybersecurity, business transformation and corporate governance.
The roles of Chief Executive Officer (CEO) and Chairman of the Board are separated to support independent oversight. The independent Chairman leads executive sessions of non-management directors, serves as the liaison between the Board and executive leadership and works with the CEO to set Board agendas and strategic priorities.
Board Composition & Diversity
Director nominees are evaluated on professional qualifications, industry knowledge, leadership experience and personal characteristics including gender, age, cultural background, nationality, race and ethnicity.
DNOW does not maintain a formal diversity policy for nominations, but diversity is a considered factor in the process, reflecting the Board’s view that a range of backgrounds and professional experiences produces better decisions.
Additional information on Board composition and governance practices is available in DNOW’s 2026 Proxy Statement.
| Average Director Age: 64.2 years |
| Average Director Tenure: 6.8 years |
| Leadership & Functional Expertise |
| Industry & Strategic Experience |
Board Committees
The Board carries out its oversight responsibilities through three standing committees composed of independent directors.

1 All Audit Committee members qualify as Audit Committee Financial Experts under SEC requirements.
Note: Board composition data are presented as of April 9, 2026, unless otherwise noted.
ESG Governance
ESG oversight at DNOW starts at the Board level with the Environmental, Social, Governance & Nominating Committee (ESG&N) and runs through executive leadership to a cross-functional, management-led ESG Committee. Established in 2019, the ESG Committee was expanded following the MRC Global acquisition to bring representation from across the combined organization into a single governance structure.
This structure connects sustainability priorities to the people responsible for delivering them. The Board sets expectations and holds accountability for ESG performance, executive leadership integrates those priorities into business strategy, and the ESG Committee translates strategy into programs, metrics and disclosures. Responsibilities at each level are outlined below.
Governance Structure
| Oversight | Board of Directors |
9 directors, 8 of whom are independent, including the Chairman. Three standing committees: Audit, Compensation, ESG&N
| Strategic Direction | Executives |
Cross-functional leadership team drawn from departments across the Company
| Implementation | ESG Committee |
Representatives from departments across the Company, overseen by members of executive management
| Performance | Employees |
Approximately 5,300 employees across global operations execute DNOW’s strategy day-to-day, monitor ESG performance and trends and implement best practices.
Note: ESG-related risks identified through this structure feed into DNOW's enterprise risk management program; see Enterprise Risk Management on page 17.
Ethics & Business Conduct
DNOW operates in more than 20 countries, and its ethics and compliance obligations vary considerably by jurisdiction. The Company manages this variance through a governance framework that sets consistent standards across all operations.
- Code of Business Conduct and Ethical Standards
- Anti-Corruption and Anti-Bribery Policy
- Trade Compliance Program
- Confidential Governance Hotline
- Human Rights Commitments
Only 0.01% of 2025 revenue came from the 20 lowest-ranked countries on Transparency International's Corruption Perceptions Index (TICPI).
| Direct Sales into the 20 lowest-ranked TICPI countries | |||||||||
|
0.01% of 2025 revenue | ||||||||
Note: 2025 TICPI data reflect legacy DNOW only; see SASB Index for legacy MRC Global.
Risk Management
Enterprise Risk Management
DNOW’s Enterprise Risk Management (ERM) program is a core component of the Company’s governance framework and strategic planning. Guided by the Committee of Sponsoring Organizations of the Treadway Commission (COSO) framework, the program provides a structured approach to identifying, assessing, prioritizing and monitoring risks and opportunities that could affect the Company’s strategic objectives, including environmental, social and governance (ESG) considerations.
Risks are evaluated across short-, medium- and long-term horizons and prioritized based on financial impact, likelihood and severity. For each identified risk, management determines an appropriate response — mitigate, transfer, accept or avoid — and assigns accountability to designated risk owners. The ERM Risk Matrix is reviewed quarterly by management and reassessed in full annually.
Risks and opportunities are identified and prioritized on three dimensions:
- Financial Impact
- Likelihood of Occurrence
- Magnitude of Consequences
The Board of Directors has overall responsibility for risk oversight. Principal risks are reported quarterly to senior management and the Audit Committee, which oversees the effectiveness of the Company’s risk management processes and internal controls. Internal Audit supports the process through risk assessments and reporting.
The ERM program covers financial, operational, cybersecurity, environmental, social, legal, regulatory, compliance and supply chain risks, including low-frequency, high-impact events such as natural disasters and major supply chain disruptions. The program is updated regularly to reflect evolving business conditions, emerging risks and stakeholder expectations.
Climate-Related Risks & Opportunities
Shifts in energy markets, regulations and customer priorities shape demand for the products and solutions DNOW provides. Climate-related risks and opportunities are assessed through a process informed by TCFD recommendations, covering both transition risks from evolving energy markets and policy developments and physical risks from severe weather and other climate hazards. DNOW evaluates transition, regulatory and physical climate risks through its ERM framework.
Cybersecurity & Data Protection
Cybersecurity Program
DNOW generates a high volume of transactions across networked systems, and the Company’s cybersecurity program is built around the NIST Cybersecurity Framework and the Center for Internet Security (CIS) Critical Security Controls. Controls include vulnerability scanning, patch management, penetration testing, firewalls, intrusion detection systems, encryption and access controls. All corporate devices on the DNOW network are monitored around the clock through a dedicated Managed Security Operations Center.
Third-party service providers requiring access to DNOW systems or data undergo a cybersecurity review before access is granted, and the Company engages independent third parties to conduct periodic information security assessments. Employees complete cybersecurity awareness training and participate in regular phishing simulations designed to reinforce secure practices and identify where additional training is needed.
Cybersecurity Governance
The Audit Committee receives regular updates on information security, data privacy, cybersecurity risks and regulatory developments. The Chief Administrative and Information Officer (CAIO) oversees cybersecurity and technology functions and reports to executive leadership and the Board. Cybersecurity risk is evaluated within the ERM program alongside other strategic, operational, financial and compliance risks. DNOW also monitors applicable cybersecurity and data privacy regulations across its operating jurisdictions and updates its policies and controls as appropriate.
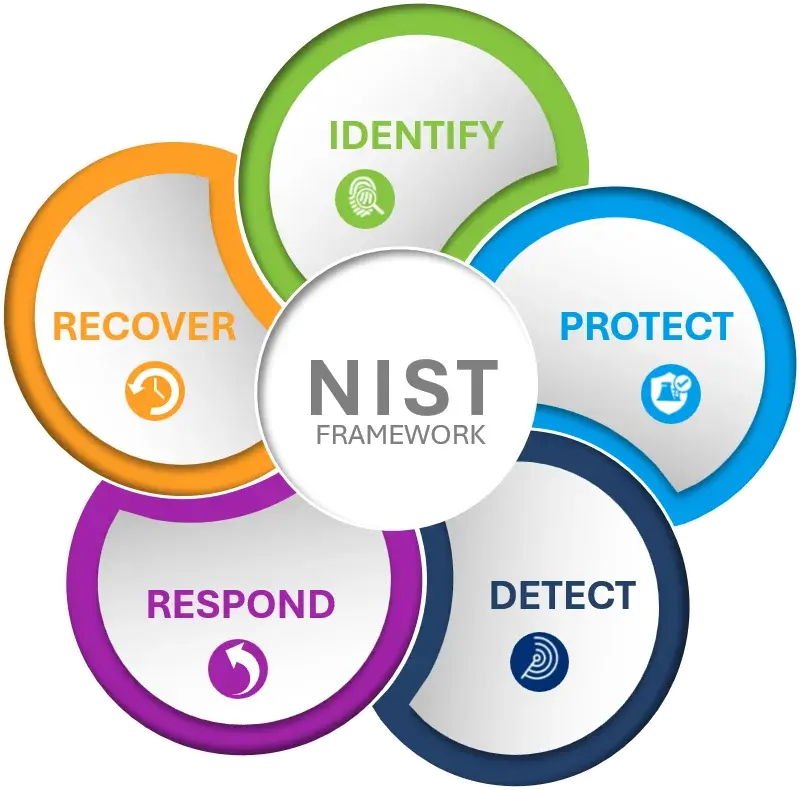
National Institute of Standards and Technology (NIST)
Incident Response
DNOW maintains a Cyber Incident Response Plan covering procedures for managing, investigating and responding to cybersecurity incidents. The plan is tested through tabletop exercises involving internal stakeholders and external advisors to evaluate response readiness and coordination across functions. In 2025, the exercise focused on a third-party compromise scenario, testing incident response capabilities, communication protocols and cross-functional coordination.
| 2025 Cybersecurity Highlights |
|
During 2025, DNOW did not experience any cybersecurity incidents resulting in a material compromise of its systems or data and incurred no material expenses related to cybersecurity breaches, regulatory penalties or settlements. The Company discloses cybersecurity incidents in accordance with applicable reporting and notification requirements.
24/7
monitoring and incident response provided by dedicated Managed Security Operations Center
ZERO
Material Cybersecurity Incidents
advanced tools improve our ability to detect, analyze and respond to security threats